By Marçal Santos, CISO and founder of SecureLeap. CISM and CDPSE (ISACA). Previously security roles at Aircall, Citibank and Talkdesk. 20+ years in cybersecurity. Leads every Secureleap penetration test engagement, delivered with vetted specialist testers.
Grey box penetration testing (also spelled gray box) is a security assessment where the tester is given partial knowledge of your system, typically user accounts for each role and an architecture overview, then attacks it the way a logged-in user or compromised partner would. It sits between black box (zero knowledge) and white box (full source code access). For a startup it typically takes about four weeks and costs $6,000 to $9,000.
Founders often assume the most realistic pentest is the one where the hacker knows nothing. In practice, a tester who knows nothing spends a large share of the budget just finding a way in. The flaws that leak customer data usually sit one step past the login, and a grey box test starts there.
Key Takeaways
- What it is: a pentest with partial, insider-level access: user accounts for every role in your app, admin roles included, plus an architecture overview, but no source code and no server or cloud admin access.
- Why startups pick it: testers spend their days behind the login, where access control and business logic flaws live, instead of mapping your perimeter. It is the pentest SecureLeap clients request most.
- The threat it models: a logged-in attacker. In 2025, valid credentials were the way in for 32% of the incidents IBM X-Force responded to, and exploitation of public-facing applications for 40%. A grey box web app test covers both paths.
- Time and cost: about four weeks end to end. A standard grey box pentest for a funded startup typically costs $6,000 to $9,000.
- Compliance fit: the report is the evidence SOC 2 auditors expect under CC4.1. For PCI DSS, Requirement 11.4 also needs internal and external network tests.
How Grey Box Testing Works
The U.S. National Institute of Standards and Technology defines gray box testing, which it also calls focused testing, as "a test methodology that assumes some knowledge of the internal structure and implementation detail of the assessment object" (NIST glossary, citing NIST SP 800-53A Rev. 5). Some knowledge, not none and not all, is the whole idea. It is also known as translucent box testing.
In a pentest, "some knowledge" usually means:
- two test accounts for every user role, from a basic member up to your in-app admin, and two customer accounts (tenants)
- an architecture overview: which services, APIs and third parties are in scope
- API documentation, if you have it
It does not include source code, or admin access to your servers, databases or cloud console. Hand over the source code and the test becomes white box.
Because the tester starts as a registered user, they skip days of guessing usernames and hunting for a login page. They start where a real attacker with a stolen password starts: inside the front door, free to probe the business logic, the data isolation and the permission checks that protect your customers.
Grey box testing also exists in software QA, where a tester with partial knowledge of the code checks that features work together. A grey box penetration test uses the same partial-knowledge idea for a different goal: proving what an attacker with a valid login can reach, and how far they can go.
How Grey Box Compares to Black Box and White Box
The three models differ in one variable: how much the tester knows going in. That variable changes the cost, the speed and the kind of flaw each one finds.
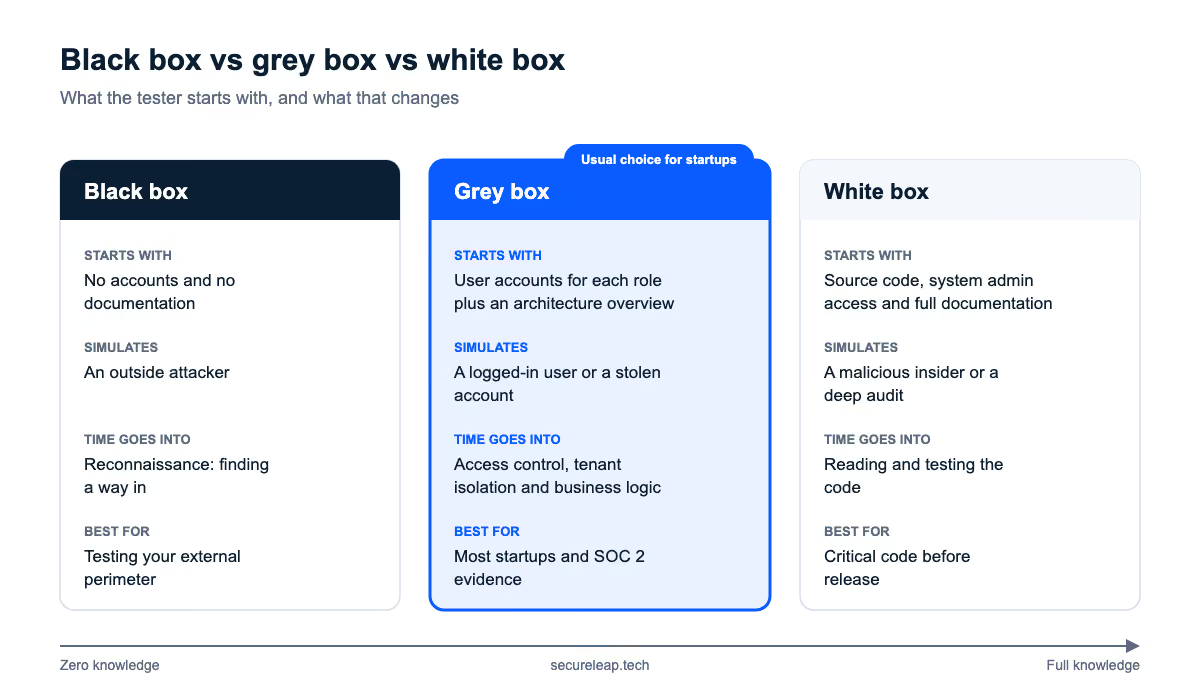
Black box testing mirrors a true outsider. It is realistic, but most of the budget goes on reconnaissance you may already understand. White box testing is exhaustive, but reading an entire codebase is slow and expensive, and rarely the right first test for a startup. Grey box sits in the middle: enough knowledge to aim the testing at what matters, without paying for a full code audit. For a wider view of every test type, see our guide to types of penetration testing.
Why Grey Box Is Our Most Requested Pentest
Grey box is the pentest SecureLeap clients request most. The reasons are practical.
1. You pay for testing, not reconnaissance
When you hand a tester credentials, you skip the slow perimeter-mapping phase and put their hours straight onto your real attack surface: payment flows, admin panels, tenant isolation and API authorization. In our grey box engagements, the highest-severity findings almost always sit behind the login, not on the public marketing site. A black box test often never reaches them.
2. It is faster than a full code review
It finishes in a fraction of the time of a white box audit, because the tester goes straight to high-risk areas instead of working through source files. For a startup that needs a clean report before a funding round or an enterprise deal, speed matters.
3. It models how breaches actually start
Most incidents IBM X-Force responded to in 2025 started in one of two ways: a stolen login (32%) or a flaw in an internet-facing application (40%). Grey box testing covers both at once: the tester attacks your public application from inside a real user account, the way an attacker with a stolen password would.
(IBM X-Force, 2026; OWASP, 2025; IBM, 2026.)
4. It answers the enterprise security review
When a large customer sends you a security questionnaire, "we run grey box penetration tests against every user role and our APIs" is a far stronger answer than "we scan our website." It shows you validated permissions, data isolation and business logic, which is what their security team is actually worried about.
"Most of the serious findings we report sit one click past the login: one customer's account reading another customer's data, or a member account calling an admin endpoint. A black box test rarely gets far enough inside to see them," says Marçal Santos, CISO at SecureLeap.
What You Hand Over Before a Grey Box Test
The rule is simple: the tester gets what a real user would have, and nothing more. Here is what to prepare for each type of target:
For every target, also agree a list of what is out of scope, testing hours, a named contact on your side, and a signed authorization before testing starts.
What not to hand over:
- Real customer data. Seed the test environment with fake records.
- Production or infrastructure admin credentials. Your app's admin role gets its own test accounts on staging, like every other role.
- Source code. It turns the test into white box, which is a different engagement.
- Staff members' personal accounts. Create dedicated test accounts, and disable them afterwards.
- Passwords in email or Slack. Share them through a password manager.
For a complete preparation list, see our penetration testing checklist.
Grey Box Web Application and API Testing
A grey box web application pentest checks whether real user accounts can see or do anything they should not. "100% of the applications tested were found to have some form of broken access control," according to the OWASP Top 10:2025, which is why this is where most of the testing time goes.
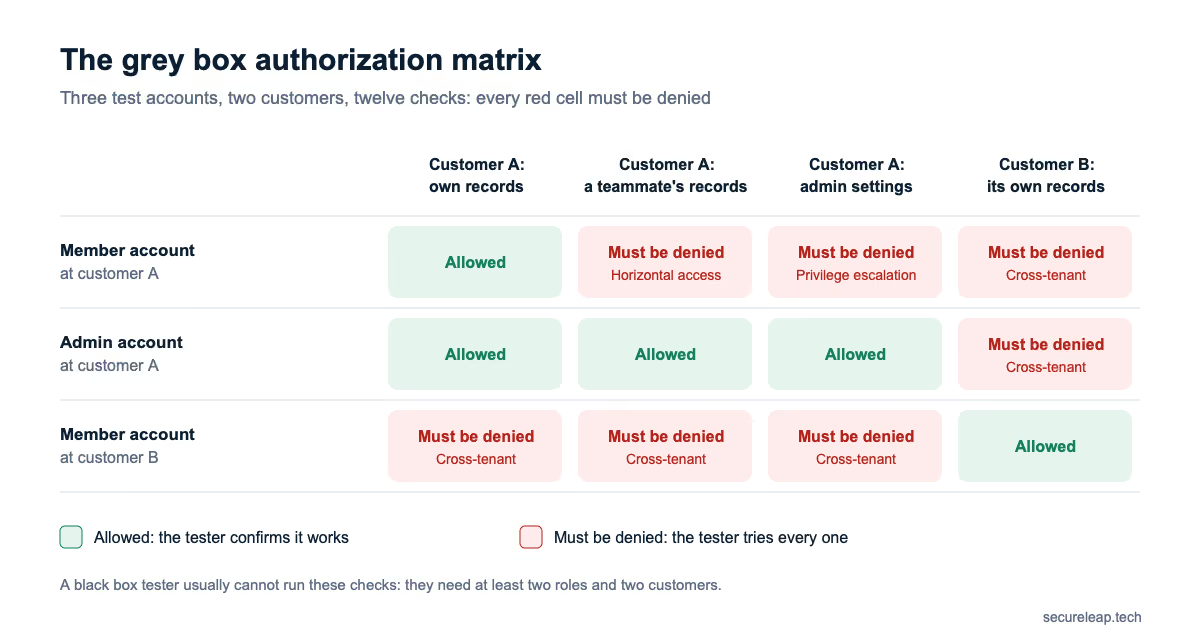
The core of the method is the authorization matrix above, shown in its smallest form: three test accounts across two customers (a member and an admin at customer A, a member at customer B), checked against four kinds of data, make twelve checks. Seven of them must be denied, and the tester tries every one. A black box tester usually cannot run these checks at all, because they need at least two roles and two customers to start.
What it typically finds
- Insecure direct object references (IDOR), called broken object level authorization (BOLA) in APIs: changing an ID in a request to read another customer's invoice, file or profile.
- Cross-tenant data access: customer A's account reaching customer B's data in a multi-tenant SaaS product.
- Privilege escalation: a member account calling an admin-only endpoint that the interface hides but the API still accepts.
- Mass assignment: adding a field such as
role=adminto a normal profile update, and the API saving it. - Business logic abuse: skipping a payment or approval step by sending requests out of order.
- Session and token flaws: tokens that keep working after logout or a password reset.
Alongside these, the most common findings in startup pentests are weak authentication, hardcoded secrets, missing security headers and misconfiguration.
The techniques behind those findings
- Authorization matrix testing: map every role against every function and try each combination.
- Tenant-swap testing: replay requests from customer A using customer B's IDs to prove data isolation.
- API parameter tampering: change object IDs, roles and prices in API calls to find BOLA and mass assignment flaws, both covered by the OWASP API Security Top 10.
- Session and token testing: check that tokens expire, stop working after logout, and cannot be forged or replayed.
- Business logic testing: send steps out of order or repeat them to bypass payments, limits and approvals.
Automated scanners can log in, but they do not reason about who should see what. That is why this kind of testing is manual at its core. Our comparison of automated vs manual penetration testing covers the trade-off, and our guide to web application penetration testing has the wider checklist.
Grey Box in Practice: Two Real Findings
Finding 1
- What it was: At a B2B SaaS provider, a low-privilege support role could change any customer's account email, creating a path to full account takeover.
- Severity: Critical
- How the test found it: A support-role token, documented as read-only, was used to call the email-change endpoint directly. Only a valid target user ID was required.
- Fix: Server-side role-based access control was enforced on the email-change endpoint, and change-notification emails to the previous address were added.
- Would a black box test have found it: No. It needed a support-role account and the documentation saying that role was read-only, and an outside attacker has neither.
Finding 2
- What it was: At a SaaS product, an AI-assisted feature that analyzes user-supplied website URLs could be pointed at internal addresses, letting the server fetch cloud metadata and return credentials (SSRF).
- Severity: Critical
- How the test found it: An authenticated account with access to the AI feature submitted an internal metadata URL and received cloud credentials in the server response.
- Fix: URL validation and allowlisting were added, internal address ranges were blocked, URL schemes were restricted, and metadata access was hardened.
- Would a black box test have found it: No. It needed a support-role account and the documentation saying that role was read-only, and an outside attacker has neither.
How Long a Grey Box Pentest Takes and What It Costs
Most startup engagements take about four weeks from planning to report, followed by a retest:
These phases map onto the five stages of a penetration test, from reconnaissance to reporting.
On price, a standard grey box pentest for a funded startup typically costs $6,000 to $9,000. Across scopes, the typical ranges in our guide to penetration testing for startups are:
These are market ranges, not SecureLeap prices: they combine published senior day rates with the testing days each scope needs.
Three things move the price:
- The size of the target: one application versus several products, APIs and environments.
- The complexity of your setup: a single web app versus microservices, multiple user roles and multi-tenant data. In practice, every extra role and tenant adds rows and columns to the authorization matrix.
- The depth of testing: an automated or AI-driven run versus manual testing that chains findings together.
For line-by-line pricing, see our penetration testing cost guide.
When Grey Box Is the Wrong Choice
Grey box is the right default for most startups, but it is not the answer to every question, and an honest tester will tell you so.
- Choose black box when your goal is to measure what a true outsider can reach with no help, for example validating your external perimeter before a product launch. Our guide to black box penetration testing covers how one runs.
- Choose white box when you need maximum assurance on a critical component, such as a new payments or cryptography module, where a line-by-line source review is worth the cost. See white box penetration testing for what it covers.
- Mind the blind spots. Because the tester does not read the source, deeply buried logic flaws can slip past. For high-stakes code, pair grey box testing with a targeted white box review.
Grey box vs an AI-driven autonomous test
AI-driven autonomous pentests cost about $3,000 to $4,000 per application. They win on speed and automation; a manual test wins on depth, finding business logic and cross-tenant flaws. Use AI for fast results and a lighter review between manual tests.
The point of a pentest is an accurate picture of risk, not a clean-looking report. Matching the method to the question is part of the job.
Common Grey Box Mistakes
- One account per role. With a single member account, the tester cannot check whether one user can read another user's data. Provide two per role.
- One tenant only. Without a second customer account, cross-tenant isolation goes untested, and in a multi-tenant product that is where one bug can expose every customer.
- Leaving the API out of scope. Your web interface is one client of the API. Attackers call the API directly, so test it directly.
- Testing production with real data. Use a staging copy with fake records. If production is the only option, agree testing hours and confirm backups first.
- Treating an authenticated scan as a grey box pentest. A scanner that logs in still cannot judge who should see what. Ask how much of the testing time is manual.
- Skipping the retest. Auditors and enterprise buyers ask whether the findings were fixed. The retest report is the proof.
- Leaving test accounts active. Disable test accounts and rotate any keys you shared once the retest is done.
Grey Box Testing and Compliance
The test maps cleanly onto the testing expectations in the frameworks startups face:
- SOC 2 does not name a pentest as mandatory, but SOC 2 auditors expect one under CC4.1 of the AICPA Trust Services Criteria, and the report should be formatted as audit evidence. (See our SOC 2 consulting.)
- ISO 27001 does not name a pentest either, but Annex A control 8.8 of ISO/IEC 27001:2022 (management of technical vulnerabilities) asks you to identify and evaluate technical vulnerabilities, and a pentest report is the usual evidence. (See our ISO 27001 consulting.)
- PCI DSS Requirement 11.4 requires penetration testing by a qualified tester following a defined methodology, internally and externally, at least once every 12 months and after significant changes. An application-layer test covers part of it; you also need network-layer testing, and segmentation testing if you rely on segmentation.
- HIPAA expects testing as part of a documented risk analysis.
Test at least once a year, and after any major release or architecture change. A single, well-scoped test can produce evidence you reuse across several of these frameworks at once.
How SecureLeap Can Help
Need a pentest quote you can compare line by line? Here is what you get:
- Led by a named practitioner: engagements are led by Marçal Santos (CISM, CDPSE), previously at Aircall, Citibank and Talkdesk.
- Certified testers: testing is carried out by certified penetration testers (OSCP, eWPTX, CPENT, CompTIA PenTest+, eMAPT, CRTP).
- Reports built as audit evidence: deliverables are formatted for direct use as SOC 2 and ISO 27001 evidence, not just a technical findings list.
- Unlimited retests for 60 days: retests after remediation are included, with no extra fees and no rebooking.
- Fixed scope and fixed price: quoted after a scoping call, before work starts, with no hourly overruns. About 3 weeks from kickoff to report.
👉 Book a Free Consultation or explore our grey box penetration testing services.
FAQ Grey Box Pentest
Is it grey box or gray box penetration testing?
Both spellings mean the same test. Grey is the common spelling in the UK and Europe, and gray is the common spelling in the US.
What is the difference between gray box and black box penetration testing?
A black box tester knows nothing and spends time mapping your perimeter from the outside. A gray box tester starts with credentials and an architecture overview, so they go straight to authenticated areas like APIs, admin functions, and business logic where the most serious flaws usually live.
What do you need to give the tester for a grey box penetration test?
Give the tester two test accounts for each user role, two separate customer accounts if your product is multi-tenant, API documentation and a staging URL. Do not share real customer data, server or cloud admin credentials, or source code.
How long does a grey box penetration test take?
Most startup engagements take about four weeks: one week of planning and scoping, two weeks of active testing, and one week of reporting and review. Larger scopes can take up to six weeks.
How much does a grey box penetration test cost?
A standard grey box pentest for a funded startup typically costs $6,000 to $9,000, and a focused test of a single web app or API runs $4,000 to $6,000. Scope drives the price, mainly the number of user roles, API endpoints and environments in the test.
Is gray box penetration testing enough for SOC 2 or ISO 27001?
For most startups, yes. A scoped gray box test gives auditors the evidence of active control testing that SOC 2 and ISO 27001 expect, though you may add a targeted white box review for especially sensitive components.