
Virtual CISO (vCISO) Services for Startups
A senior security leader who owns your security program, without the full-time hire. Strategy, policies, compliance, and a named person your customers and board can talk to.

You’re in good company




Why startups hire a virtual CISO
At some point security stops being something everyone does a little of and starts needing an owner.
A virtual CISO gives that ownership to someone whose job it is. You get senior security judgment on the decisions that matter: what to fix first, what risk to accept, and what to escalate. Your engineers get direction instead of another side project.
A customer's security questionnaire arrives and nobody knows who should answer it.
Policies exist as templates, but nobody enforces or updates them.
SOC 2 or ISO 27001 has become a deadline instead of a someday.
Investors or the board ask who is responsible for security, and the honest answer is "the CTO, sort of."
Engineers make risk decisions on their own because no one else will.
What our vCISO services include
Every engagement covers the leadership layer of your security program. What goes into the roadmap depends on your risks and your customers, not on a template.

Security assessment and roadmap
Where you stand today against the frameworks your buyers ask about, and a prioritised plan to close the gaps.

Policies and documentation your team will follow
Written for a startup, kept current, and mapped to SOC 2, ISO 27001, or both.

Clear security ownership
Defined roles and responsibilities, so security stops being "everyone's job" and starts being someone's.

Vendor and third-party risk
Due diligence on the SaaS tools and partners that hold your data.

Customer security reviews
Fast, accurate answers to questionnaires, and a security leader who joins the call when a prospect's procurement team wants to talk to one.

Incident response governance
A plan that is written, assigned, and tested before you need it.

Board and investor reporting
Security risk translated into decisions your leadership can act on.

Compliance program leadership
SOC 2, ISO 27001, ISO 42001, NIS2, and GDPR scoped, driven, and kept audit-ready.
vCISO engagement models and pricing
Three levels of involvement, and affordable plans aligned with what your business needs.
Navigator
Security guidance, risk decisions, and roadmap
Co-Pilot
Everything in Navigator, plus we write and maintain your policies, documentation, and compliance evidence
Captain
Full executive support: your security leader in front of customers, auditors, and the board, running the program end to end
How Secureleap's vCISO service works
Four steps from understanding your business to making security an asset that helps you close more deals.
Business needs
We start with what your business needs from security: the customers you sell to, the frameworks they expect, and the goals security has to support.
Security assessment
We review your current practices, controls, and weaknesses, and measure them against those needs.
Roadmap
A prioritised plan that tackles the issues found and moves you toward your goals, with clear owners and timelines.
Business support
We keep supporting the business as it grows, and turn security into an asset that helps you close more deals.
We work inside your tools
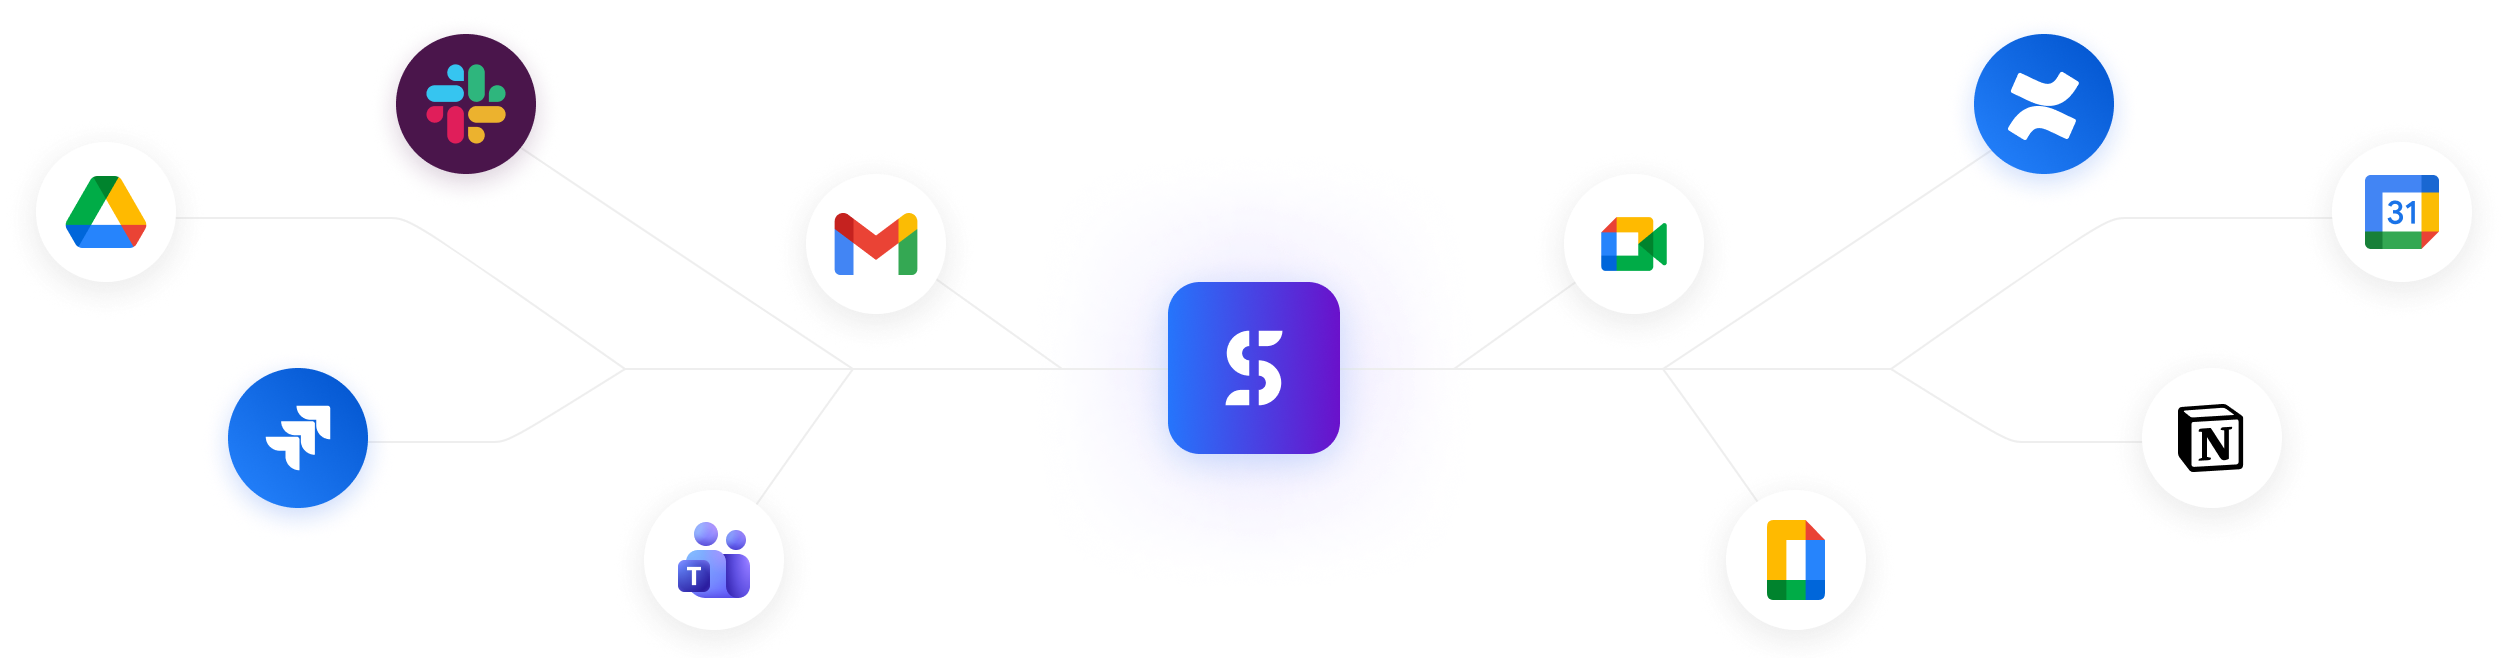
Slack, your ticketing system, your document workspace, and your GRC platform if you have one. There is no new portal to log into. We adapt to your existing processes and requirements, not the other way round.
vCISO vs full-time CISO vs GRC tool
Don’t Just Take Our Word For It
Hear from businesses who have stood in your shoes, before making their way to your most ambitious goals, with the help of our expertise.
vCISO Relevant Articles


Frequently Asked Questions
Navigate the complex world of cybersecurity with confidence and clarity.
A virtual CISO is an outsourced security executive who provides the same strategic leadership as a full-time Chief Information Security Officer on a flexible basis. A vCISO sets security strategy, manages risk, owns the compliance program, and reports to leadership, without the cost of a permanent executive hire. See our full guide: what is a vCISO.
A full-time CISO is a permanent internal executive, usually justified once a company has the scale and complexity to need dedicated security leadership every day. A vCISO provides the same function sized to what your company needs now, and scales as you grow. Read our vCISO vs full-time CISO comparison.
Secureleap's Navigator plan starts at $3,999 USD per month. Co-Pilot and Captain plans are priced to your needs, based on the number of frameworks, company size, and how much execution you want us to own. For market ranges, check our vCISO cost guide.
Yes. Most clients choose a monthly retainer, but we also run fixed-scope projects (for example, a security assessment or an ISO 27001 readiness program) and hourly engagements for occasional advice.
Yes. Certification is the most common reason startups bring in a vCISO. We scope the right framework, prepare you for the audit, manage evidence collection, and act as your security leadership throughout. Where both frameworks apply, we map overlapping controls so you implement them once.
Yes. As AI becomes part of more products, governing it responsibly is now part of a CISO's scope. We assess AI-specific risks and can guide you through ISO 42001 and related AI governance requirements.
Yes. A vCISO does not replace your team. It gives them direction and fills the gaps in expertise. If you already have engineers or a security hire, your vCISO helps them prioritise and scale their impact instead of duplicating their work.
Yes. We work inside Slack, your ticketing and documentation tools, and whatever GRC platform you use. We adapt to your processes and requirements rather than asking you to adopt ours.
Based in Portugal, Secureleap works with startups worldwide, mainly in the EU, UK, and US.
Prefer to start with an email?
Send us a message, and we’ll respond promptly.
Ready to give security an owner?
Book a call and we will map your current gaps, your customers' requirements, and the engagement model that fits.
